Data Breaches
Encryption in Transit: Protect Data Moving Across Networks
Encryption in transit secures data while it moves between systems, but it fails to protect information once it reaches its final destination or rests in storage.
Everything Patch Observer has reported about network security: 7 stories, newest first. Part of our Tech News coverage.
Encryption in transit secures data while it moves between systems, but it fails to protect information once it reaches its final destination or rests in storage.
Linux firewall rules process traffic sequentially from top to bottom, meaning rule order determines security outcomes more than individual rule content.
Network access control stops devices from connecting before they pass a security check, preventing infected machines from spreading malware across your internal infrastructure.
Most firewall failures stem from conflicting rule logic and hidden statefulness, not from missing blocks or weak encryption settings.
Data loss prevention works by inspecting content patterns, not just blocking file types, to stop sensitive data from leaving your network undetected.
Moving security logic to the edge reduces latency but creates thousands of unmanaged attack surfaces that traditional perimeter defenses cannot see or control.
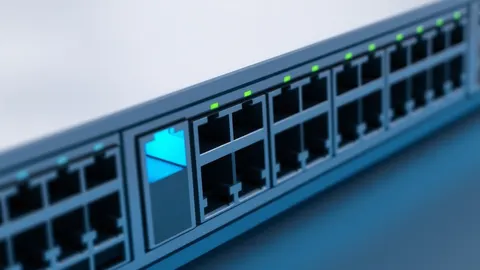
Most security breaches occur not because hackers break encryption, but because administrators leave unused network ports open like forgotten side doors.